You think you're hiring a remote developer based in Melbourne or Sydney. You check their code, review their GitHub commits, and chat over Slack. Everything looks clean. But thousands of miles away, an operative sitting in a state-sponsored bureau in Pyongyang is cashing your paychecks, funneling hard currency straight into ballistic missile tests and nuclear warhead development.
This isn't dystopian fiction. It's the harsh operational reality that forced the Australian government to drop targeted financial sanctions on two key individuals and two front companies tied directly to the North Korean fake IT workers scheme. Foreign Minister Penny Wong didn't mince words when announcing the crackdown. Canberra is drawing a hard line against the international networks enabling North Korea to bypass United Nations Security Council resolutions through fraudulent employment.
Let's be honest. For years, tech companies treated remote hiring as a casual, borderless free-for-all. You needed code written fast, so you posted a job board listing, interviewed over video call, and shipped a laptop. State-sponsored threat actors noticed this administrative blind spot. They realized that Western companies hiring remote contractors often cared more about shipping features than verifying physical identities.
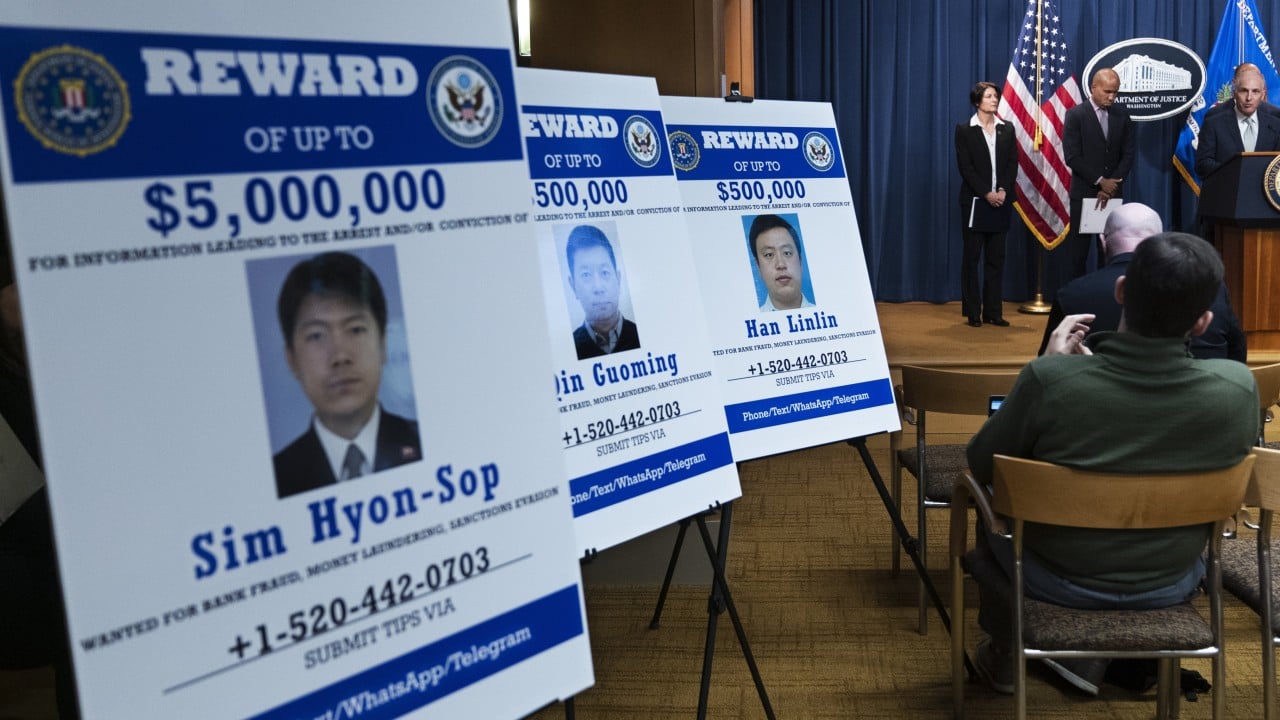
The recent Australian sanctions expose specific architects of this operation. Canberra has targeted Yu Pu Ung and Sim Hyon Sop, alongside two critical corporate fronts: Korea Mangyongdae Computer Technology Company and Chinyong Information Technology Cooperation Company. These aren't random rogue hackers sitting in basements. They are part of an organized state apparatus designed to deploy thousands of skilled IT workers across global freelance platforms and remote enterprise contracts.
How the Remote IT Worker Scam Actually Operates
The mechanics of this scheme are both brazen and terrifyingly simple. North Korea trains thousands of elite computer science graduates, coding prodigies who spend their entire lives mastering software engineering specifically to generate illegal revenue for the Kim regime. Once trained, these workers need a way to bypass international sanctions that ban North Korea from exporting labor.
They do this by adopting stolen identities.
The Australian Sanctions Office issued explicit warnings detailing how these operatives obtain stolen and doctored Australian driver's licences and passports. They acquire genuine identification documents from unsuspecting citizens or black-market brokers. Then, they doctor these documents or use deepfake video technology during interviews to pass verification checks.
Once hired, they connect to employer networks using "laptop farms." Instead of logging in from an Australian suburb, the developer connects through Virtual Private Networks (VPNs) routed through local proxy devices stationed inside Australia. An accomplice physically located in the target country hosts these proxy routers in residential apartments, keeping the company's IT monitoring tools convinced that the developer is sitting right where they claim to be.
You get your React components or Python scripts delivered on time. The worker gets paid in cryptocurrency or routed fiat currency. And Pyongyang gets the hard cash required to finance weapons of mass destruction.
Following the Money Straight to the Nuclear Program
Why would a regime under crushing international sanctions care about freelance coding gigs? Scale.
Multiply one developer earning six figures by thousands of operatives working simultaneously across the United States, Europe, Australia, and Asia. The revenue stream is staggering. Intelligence agencies estimate that these cyber operatives rake in hundreds of millions of dollars every single year.
This isn't petty cybercrime or ransomware extortion where hackers demand Bitcoin from hospitals. This is institutional labor export disguised as legitimate remote work. Every dollar earned by a North Korean developer working a remote Australian software engineering contract goes directly into state coffers. It bypasses global financial controls entirely.
When international observers look at North Korea's rapid advancements in intercontinental ballistic missiles and nuclear warhead miniaturization, they often wonder how an impoverished nation struggling with domestic famine affords such high-tech weaponry. The answer is sitting in remote tech sprints, cloud architecture setups, and freelance web development contracts. Your tech stack might inadvertently be funding their next missile test.
The Heavy Legal Hammer Dropping Down on Accomplices
Canberra isn't just issuing polite diplomatic warnings anymore. The Australian government means business, and the penalties for getting caught aiding these networks are severe enough to ruin careers and sink businesses.
Breaching these sanctions by making an asset available to a listed person or entity carries staggering legal consequences. Individuals face up to 10 years in jail and financial penalties reaching up to $910,000. For corporations, the penalties skyrocket to $3.64 million per violation.
If your human resources or procurement department accidentally contracts with a front company or processes payments for a sanctioned individual, ignorance is not a valid legal defense. The Australian Sanctions Office expects rigorous compliance and thorough background checks. If you fail to vet your remote contractors properly, you might find federal investigators knocking on your corporate office doors.
This recent action builds upon previous multi-nation crackdowns. Last November, Australia joined international partners in sanctioning prominent North Korean hacking syndicates like the Lazarus Group, its Andariel offshoot, and the espionage-focused Kimsuky unit. While those previous rounds targeted direct state-backed cyber attacks and malware campaigns, this latest move specifically attacks the economic engine room: the personnel placement networks and financial fixers funding the entire apparatus.
What Tech Companies Are Missing in Their Hiring Protocols
Most corporate hiring managers and startup founders are completely unprepared for state-sponsored infiltration. They rely on traditional HR playbooks designed for a world where people walked into physical offices with local resumes and verifiable tax file numbers.
That world is gone.
If you want to protect your intellectual property, avoid severe financial penalties, and stop funding totalitarian regimes, you have to completely overhaul how you onboard remote talent. Stop trusting PDF resumes and remote video interviews at face value.
Implement mandatory in-person identity verification or trusted third-party video KYC (Know Your Customer) checks that require government-issued biometric authentication. Look closely at behavioral anomalies. If a candidate's GitHub commit history shows massive activity spikes during unusual time zones, or if their webcam feed has suspicious visual artifacts, pause and investigate immediately.
Audit your payroll pathways. Are you paying contractors through opaque cryptocurrency wallets or shell companies registered in high-risk jurisdictions? Demand direct banking details tied to verified local identities.
Security isn't just a firewall problem anymore. It's an HR problem. It's a procurement problem. It's an operational vigilance problem.
Review every contractor on your roster today. Verify their physical presence, scrutinize their documentation, and ensure your business isn't accidentally serving as a funding conduit for foreign weapons programs.
How North Korean Agents Are Infiltrating Australian Companies
This video provides an expert breakdown of how state-sponsored threat actors bypass conventional corporate hiring defenses to secure remote engineering positions.